As of 21 September 2026, the latest Presidency compromise text on the Digital Omnibus provides an increasingly clear indication of where the Council negotiations on GDPR reform are heading. The document, circulated ahead of the Antici Group (Simplification) meeting on 25 September, contains further changes to some of the most contested provisions. Some are constructive, but taken as a whole, the evolution of the GDPR text raises a more fundamental concern. There is little visible evidence that the competing considerations which prompted this reform, including simplification, legal certainty, innovation and European competitiveness, are receiving the same weight as the concerns expressed by the EDPB and EDPS about preserving the existing reach and protections of the GDPR.
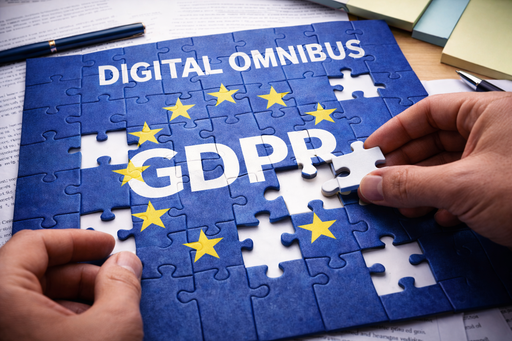
The Digital Omnibus was not conceived as a routine exercise in maintaining the status quo. Its purpose is to address regulatory complexity and provide greater certainty for organisations operating in Europe’s data economy. The Commission describes simplification as central to its competitiveness agenda, with clearer rules intended to support investment, innovation and growth. That policy direction did not emerge in isolation. Letta argued that Single Market regulation should facilitate, not hinder, economic activity and innovation, while Draghi identified Europe’s innovation and productivity challenges as central to its future competitiveness. The question, therefore, is not whether the GDPR should continue to provide a high level of protection. It should. The question is whether the Council is making sufficient use of this legislative opportunity to make that protection clearer, more proportionate and more workable in practice.
Nowhere is the evolution of the negotiations more instructive than in the debate over the definition of personal data. The Commission started with a relatively simple proposition: clarify Article 4 itself. Its proposal sought to make explicit that information should not necessarily constitute personal data for every entity merely because somebody, somewhere, possesses additional information capable of identifying the individual. The relevant question would instead turn on whether the particular entity has means reasonably likely to be used to identify that person. That approach attempted to provide greater legal certainty about one of the GDPR’s most fundamental questions: when does the Regulation apply at all?
The EDPB and EDPS strongly opposed the proposal in their February Joint Opinion. They argued that it would significantly narrow the concept of personal data and urged the co-legislators not to adopt the proposed changes to the definition. The Council’s subsequent evolution is revealing.
Under the Cyprus Presidency, the attempt to clarify Article 4 was abandoned in favour of a new Article 29a dealing specifically with pseudonymised data and identifiability. That approach already represented a significant shift. Instead of resolving the issue at its source, namely the definition determining the material scope of the GDPR, the Council attempted to deal with particular circumstances in which pseudonymised data might cease to be personal data.
When the Irish Presidency took over in July, it reopened the question. Member States were invited to consider whether the Council approach was actually delivering the intended legal certainty and simplification. The latest answer is Article 25a.
There is undoubtedly progress in the provision. The Council now accepts expressly that pseudonymised data disclosed to a third party may not constitute personal data for that party where the individual is not identifiable from its perspective. The accompanying recital recognises that pseudonymisation can effectively prevent persons other than the controller from identifying the data subject and that identifiability should be assessed against practical factors including technical measures, legal prohibitions, cost, time and effort.
But the surrounding qualifications reveal how reluctant the Council remains to follow that principle to its logical conclusion. The latest recital says that identifiability depends on the circumstances, including who controls the data, the relationship between the parties and whether the recipient processes the data on behalf of another party. It then preserves GDPR application where a processor handles pseudonymised data for a controller for whom the individual remains identifiable. The text also brings onward disclosures within the personal data framework where the subsequent recipient holds, or can reasonably obtain, the means of identification.
There are legitimate reasons for addressing those situations. A purely formal relative approach could create opportunities to construct processing arrangements designed to circumvent GDPR obligations, including potentially the rules governing international transfers. That risk should not be dismissed. Preventing circumvention, however, does not require abandoning the underlying principle that personal data should ultimately be defined by whether a natural person is realistically identifiable in the relevant circumstances.
This is where the evolution from Article 4, through Article 29a, to Article 25a becomes significant. With each iteration, the Council has moved further from a straightforward clarification of what personal data is, towards increasingly detailed rules governing when the GDPR should continue to follow data through a processing ecosystem. The distinction is subtle but important. The policy question risks shifting from whether an individual is identifiable in practice to whether maintaining regulatory coverage of the processing chain is desirable.
If that happens, the concept of personal data begins performing a function for which it was not designed. The boundaries of the Regulation become determined partly by a desire to preserve supervisory reach rather than exclusively by the characteristics of the information and the realistic possibility of identification. That may produce wider GDPR coverage, but it does not necessarily produce greater legal certainty.Nowhere is the evolution of the negotiations more instructive than in the debate over the definition of personal data. The Commission started with a relatively simple proposition: clarify Article 4 itself. Its proposal sought to make explicit that information should not necessarily constitute personal data for every entity merely because somebody, somewhere, possesses additional information capable of identifying the individual. The relevant question would instead turn on whether the particular entity has means reasonably likely to be used to identify that person. That approach attempted to provide greater legal certainty about one of the GDPR’s most fundamental questions: when does the Regulation apply at all?
The EDPB and EDPS strongly opposed the proposal in their February Joint Opinion. They argued that it would significantly narrow the concept of personal data and urged the co legislators not to adopt the proposed changes to the definition. The Council’s subsequent evolution is revealing.
Under the Cyprus Presidency, the attempt to clarify Article 4 was abandoned in favour of a new Article 29a dealing specifically with pseudonymised data and identifiability. That approach already represented a significant shift. Instead of resolving the issue at its source, namely the definition determining the material scope of the GDPR, the Council attempted to deal with particular circumstances in which pseudonymised data might cease to be personal data.
When the Irish Presidency took over in July, it reopened the question. Member States were invited to consider whether the Council approach was actually delivering the intended legal certainty and simplification. The latest answer is Article 25a.
There is undoubtedly progress in the provision. The Council now accepts expressly that pseudonymised data disclosed to a third party may not constitute personal data for that party where the individual is not identifiable from its perspective. The accompanying recital recognises that pseudonymisation can effectively prevent persons other than the controller from identifying the data subject and that identifiability should be assessed against practical factors including technical measures, legal prohibitions, cost, time and effort.
But the surrounding qualifications reveal how reluctant the Council remains to follow that principle to its logical conclusion. The latest recital says that identifiability depends on the circumstances, including who controls the data, the relationship between the parties and whether the recipient processes the data on behalf of another party. It then preserves GDPR application where a processor handles pseudonymised data for a controller for whom the individual remains identifiable. The text also brings onward disclosures within the personal data framework where the subsequent recipient holds, or can reasonably obtain, the means of identification.
There are legitimate reasons for addressing those situations. A purely formal relative approach could create opportunities to construct processing arrangements designed to circumvent GDPR obligations, including potentially the rules governing international transfers. That risk should not be dismissed. Preventing circumvention, however, does not require abandoning the underlying principle that personal data should ultimately be defined by whether a natural person is realistically identifiable in the relevant circumstances.
This is where the evolution from Article 4, through Article 29a, to Article 25a becomes significant. With each iteration, the Council has moved further from a straightforward clarification of what personal data is, towards increasingly detailed rules governing when the GDPR should continue to follow data through a processing ecosystem. The distinction is subtle but important. There is a risk that the policy question ceases to be whether an individual is identifiable in practice and becomes whether maintaining regulatory coverage of the processing chain is considered desirable.
If that happens, the concept of personal data begins performing a function for which it was not designed. The boundaries of the Regulation become determined partly by a desire to preserve supervisory reach rather than exclusively by the characteristics of the information and the realistic possibility of identification. That may produce wider GDPR coverage, but it does not necessarily produce greater legal certainty.
Article 25a matters beyond the definition of personal data because it reflects a broader trend in the negotiations. Scientific research provides another example. The Commission proposed introducing a definition for the first time, expressly recognising research conducted for commercial purposes and technological development. The Council text has progressively surrounded that concept with additional expectations concerning methodology, ethical standards, research integrity, autonomy and independence, transparency and verifiability. The latest recital continues to contemplate making research results publicly available, albeit subject to legitimate limitations including intellectual property and trade secrets.
There are reasonable policy arguments behind many of these concepts. Cumulatively, however, they risk turning what was intended to be a clarifying definition into another area requiring organisations to determine whether their activities satisfy an increasingly elaborate regulatory conception of what qualifies as scientific research. The direction is difficult to reconcile with an exercise intended to simplify the GDPR and provide greater certainty for research and innovation.
The same dynamic is evident in AI. The Commission originally proposed Article 88c to provide greater certainty around legitimate interests as a legal basis for processing personal data in AI development and operation. The EDPB and EDPS considered a specific provision unnecessary because legitimate interests can already apply in appropriate circumstances. The operative provision subsequently disappeared from the Council text.
The latest compromise does represent some movement. It now expressly recognises in the recitals that AI development and use may rely on legitimate interests under Article 6(1)(f), while describing considerations relevant to the balancing exercise. That is useful, but it remains a considerably more cautious intervention than creating clear legislative certainty about an issue of obvious importance to Europe’s AI ambitions. A risk-based framework does not require the removal of safeguards, nor does supporting AI development mean creating an unrestricted legal basis for processing. But where uncertainty itself is inhibiting investment and innovation, confirming that an existing legal basis may apply, subject to an increasingly detailed set of considerations, only partially addresses the problem. There are nevertheless areas where the Council is delivering meaningful simplification, and these should be recognised. The development of a higher threshold for breach notification, additional time for notification and greater harmonisation of procedures are practical improvements. Work on abusive data subject requests and harmonisation around DPIAs also demonstrates that simplification and strong data protection are not mutually exclusive. In fact, these provisions demonstrate that the Council can preserve effective protection while making GDPR compliance clearer and more proportionate.
The concern with the emerging compromise is therefore not that the Council is listening to the EDPB and EDPS. It should listen to them. They possess considerable expertise and have an institutional role in safeguarding data protection. The concern is that there is little evidence from the evolution of the text that other perspectives are being given equivalent weight.
The February Joint Opinion approached the Commission proposal primarily through the lens of data protection: whether simplification affected the level of protection, whether proposed changes might narrow the GDPR’s scope and whether existing safeguards should be preserved. That is entirely understandable given the mandates of the institutions concerned. The Council has a broader task. It must consider data protection alongside the functioning of the Single Market, Europe’s capacity to innovate, the practical experience of organisations applying the GDPR, the need for legal certainty and the political commitment to reduce unnecessary regulatory complexity.
Those considerations are not external to the Digital Omnibus. They are the reason it exists. The latest compromise itself recalls that the Commission’s simplification programme is intended to strengthen competitiveness while reducing regulatory burdens and describes the Omnibus amendments as providing regulatory clarifications that stimulate innovation and reduce compliance costs. The wider policy agenda is equally clear. Letta called for tackling unnecessary and incoherent regulatory burdens and argued for a framework better able to support innovation. Draghi’s analysis has become an important foundation of the EU’s competitiveness strategy. The Commission has similarly placed simplification and regulatory clarity at the centre of its economic agenda.
The GDPR cannot be insulated from that discussion. Ten years after its adoption, there is enough practical experience to distinguish between protections that genuinely safeguard individuals and legal uncertainty that increases compliance costs without producing a corresponding benefit for data subjects. Making that distinction is not deregulation. It is part of the normal evolution of a mature regulatory framework. Article 25a demonstrates the difficulty particularly clearly. There is a legitimate need to prevent artificial arrangements designed to circumvent the GDPR. But that objective should not lead to a concept of personal data that expands simply because maintaining regulatory control over every participant in a processing chain is considered safer. The legal test should remain anchored in the reality of identifiability. Otherwise, the debate risks shifting from the protection of individuals towards preservation of the regulatory perimeter itself.
The Digital Omnibus provides an opportunity to recalibrate that balance. The Council has already demonstrated in some areas that meaningful simplification can coexist with strong protection. It should bring the same approach to the more difficult questions. The progression from Article 4 to Article 29a and now Article 25a suggests that, so far, the opposite has happened on one of the most consequential issues in the reform. Rather than progressively clarifying the boundary of the GDPR, successive texts have progressively qualified it.
There is still scope in the negotiations for a different approach, but it requires the Council to look beyond the established data protection perspective and bring the wider European policy agenda fully into the discussion. Protecting individuals and enabling innovation are not objectives between which Europe should have to choose. Developing a framework that achieves both should be the ambition for the next generation of privacy.
24 September 2026
Square de Meeûs 18
1050 Brussels | Belgium
info@privacynext.eu
Copyrights © 2026 PrivacyNext.eu | Privacy Policy | Cookie Policy Webdesign & Development by ALYS