On 12-13 October, Privacy Next attended the 2026 Confederation of European Data Protection Organisations (CEDPO) DPO Conference in Brussels. The conference theme was “Is Simplicity the Key? Assessing the EU Digital Omnibus and the Future of GDPR.” The event brought together a diverse range of voices including policymakers, regulators, DPOs, industry representatives, and other privacy experts.
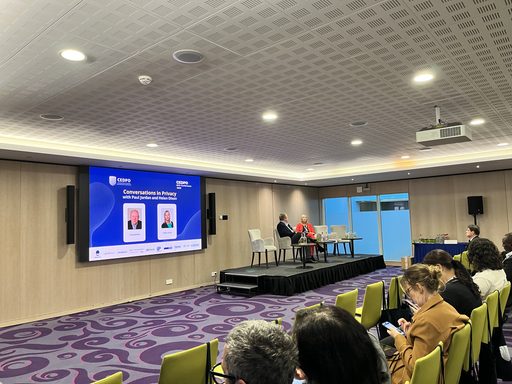
The overall message from CEDPO 2026 was not that GDPR should be weakened, but that Europe must improve the practical operation of its digital regulatory framework. Further, the event made clear that the DPO role increasingly sits at the intersection of privacy, AI, cybersecurity, data governance, and innovation strategy. As the future of data protection in the EU continues to be debated, the conference made clear that regulatory coherence across legislation is necessary to support how organisations operate and that a risk-based governance approach is needed for GDPR implementation.
One of the strongest themes throughout the conference was the continuing evolution of the Data Protection Officer role. Speakers highlighted how the ever-growing data-based economy is creating a transition for DPOs from compliance specialists to broader governance professionals. In many organisations, DPOs are now not limited to navigating the GDPR, with responsibilities extending to AI regulation, data governance frameworks, and other emerging digital rules. This makes clear that data protection is no longer a standalone legal function but an essential component of corporate strategy and innovation governance.
The ongoing discussions over the Digital Omnibus were a major part of the event. Several speakers expressed the need to address areas where data protection regulation has generated excessive complexity, legal uncertainty, and unnecessary costs. At the same time, the high levels of data protection the EU has achieved must be maintained. To achieve this, it is imperative to reform the GDPR so it works more effectively in practice while preserving legal certainty. For addressing legal certainty, attention was given to the matter of divergent interpretation by regulators across the Member States, hindering the free flow of data, a stated objective of the GDPR.
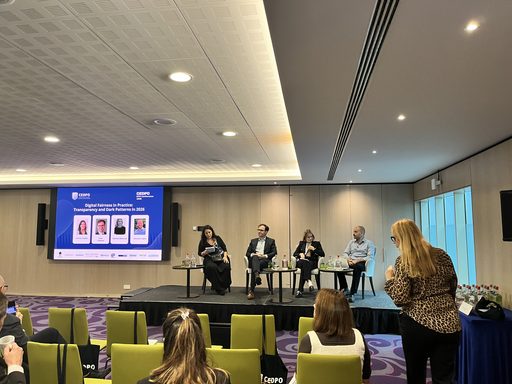
Inconsistent implementation and divergent interpretations are most apparent in relation to the definition of personal data. Multiple speakers argued that the definition has become subject to increasingly broad interpretation, creating a variety of obstacles for organisations. Further attention was given to the means by which regulators appear to be overly reliant on consent as a lawful basis for processing data when there are multiple legal bases that can be used. Legitimate flexibility should be possible but remains an underused principle in practice. This is especially clear in scientific research, where speakers highlighted persistent uncertainty about the scope and application of the GDPR’s research provisions. Participants argued that clearer definitions and more consistent application are necessary to support innovation, particularly in health research and data-intensive scientific projects.
AI governance was also a prominent topic during the conference. Discussions recognised that organisations face growing challenges in operationalising AI governance against a backdrop of overlapping regulatory requirements, including data protection. It was expressed that effective AI governance requires clear accountability structures, transparency regarding authorised AI use, and appropriate oversight mechanisms. Going forward, as AI governance and data governance converge into a single policy conversation, frameworks need to balance rights protection with competitiveness, innovation, and the technological advancements being delivered by AI.
For Privacy Next, the conference underscored the growing policy consensus that effective data governance must move beyond compliance and become an enabler of business innovation, with DPOs playing a key role in responsible data use. Attention needs to continue to focus on furthering regulatory coherence, legal certainty, and creating conditions that allow organisations to generate value from data while preserving trust and accountability.
19 October, 2026
Square de Meeûs 18
1050 Brussels | Belgium
info@privacynext.eu
Copyrights © 2026 PrivacyNext.eu | Privacy Policy | Cookie Policy Webdesign & Development by ALYS